Chart · loading
Loading page…
Loading page…
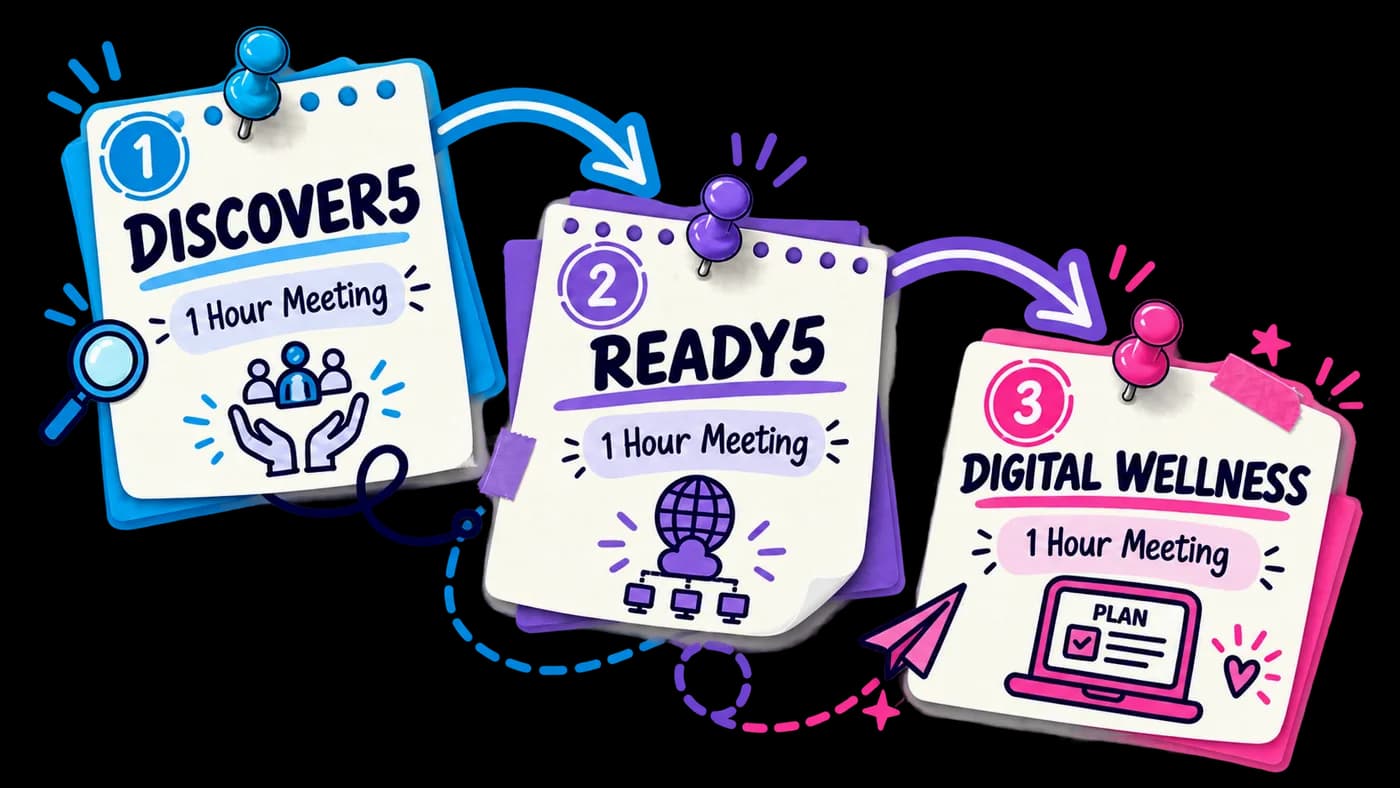
Our Three Meeting Process
In just three meetings, your nonprofit or tax-exempt organization gets a clear picture of where you stand and how to fix it at no cost to qualifying organizations.
File · CRC/003 · The engagement
§ 01 · The engagement
Every engagement runs the same way. Pick a step to see who needs to be in the room, how long it takes, and what you walk away with.
Meeting 1 of 3 · Business risk assessment
A conversation about how your organization runs - not a technical audit. There is no need to bring an IT admin. Bring a COO, a CFO, a board member if you like; our interns sign up to attend too, so they learn about your mission while building their own skills.
Personnel
Who does the work, and from where?
Finances
What can you actually spend on this?
Operations
What would stop if the systems stopped?
IT support
Who do you call when something breaks?
Governance
What happens if it goes wrong tomorrow?
File · CRC/003 · FAQs
§ 02 · FAQs
Dollar figures below cite NetDiligence 2024.
Three meetings, each one (1) hour long, at your location, ours, or virtual.
Ransomware and business email compromise are the leading causes of loss in cyber insurance claims. The average cost of a cyberattack for a small-to-medium organization is around $274,000.*
Yes. Attackers are indiscriminate and their ransom demands are rising. They target organizations ranging from under $17K in annual revenue to over $230B.*
Working backwards from successful attacks. Forensics investigations of incidents repeatedly land on the same five missing capabilities: identity, endpoint, email, edge, and response.
*Figures above are summarized from the NetDiligence Cyber Claims Study 2024 Report.
File · CRC/003 · Close
§ 03 · Get started
The intake takes about five minutes. It tells us enough to schedule a Discover5 conversation and start the workup.
Book Your Assessment