D5 · Business risk
Discover5
Executive-led · 36 findings across 5 areas
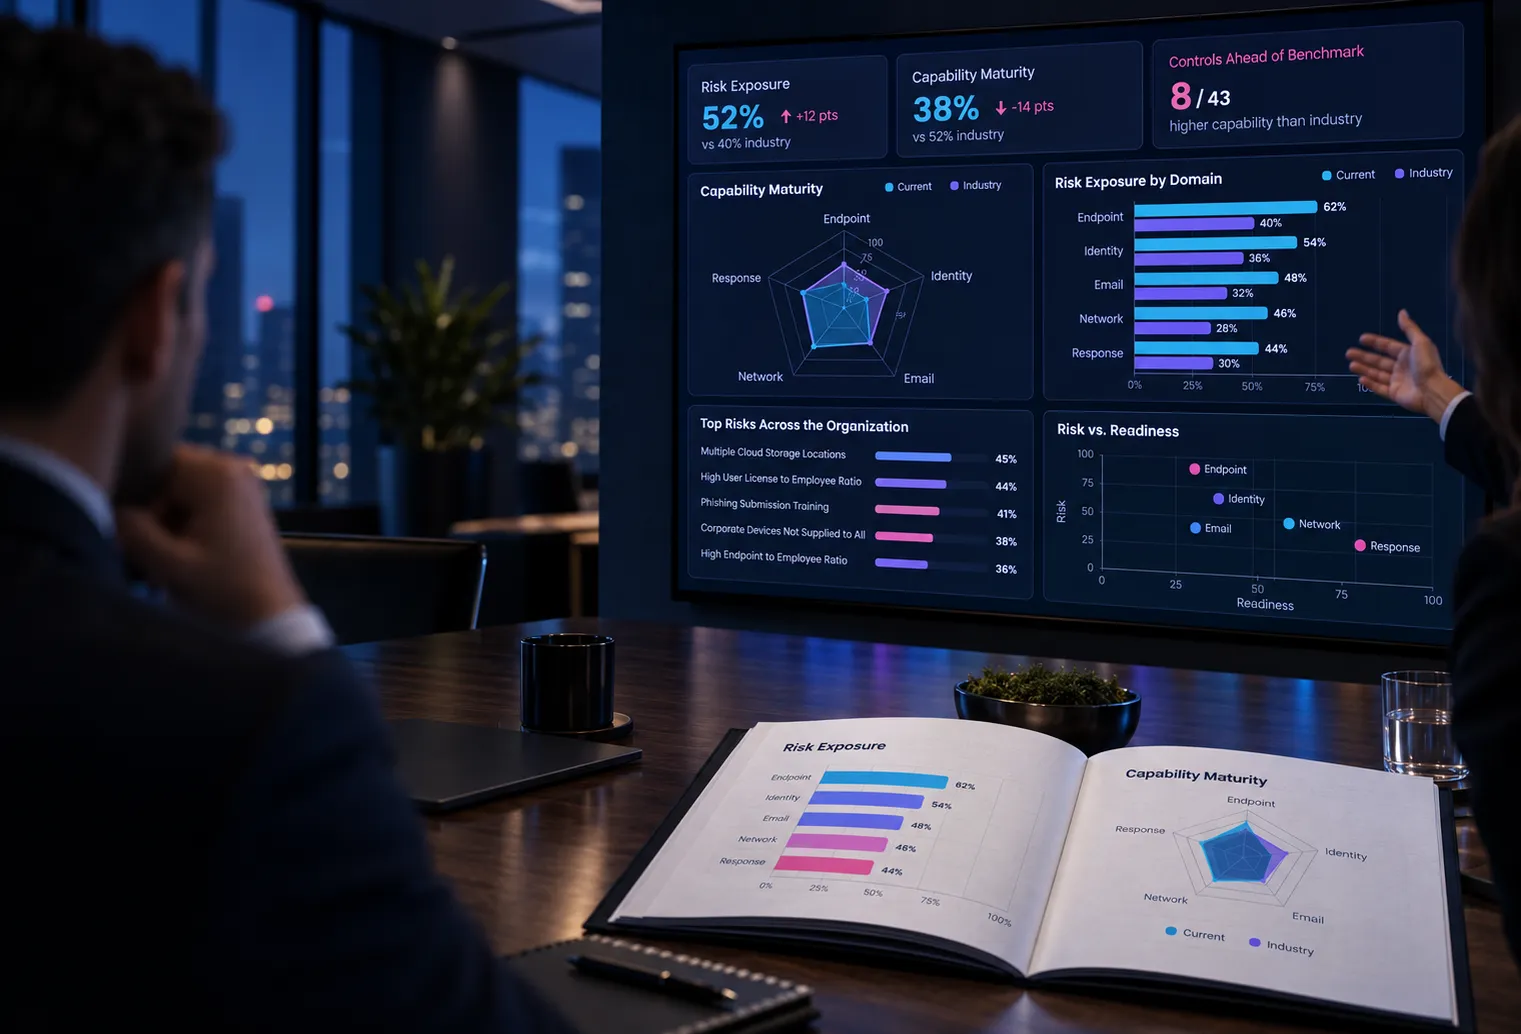
A structured business-risk assessment run as a conversation with organizational leadership. It examines who has access to systems and data, how cyber spend is prioritized, what the business actually runs on, how much PII sits in the environment, and whether anyone owns the security program. A higher score means more risk present.
- PersonnelNon-employee access, contractor ratios, endpoint and personal-device sprawl6
- FinancesIT spend as a share of revenue, budget trend, card-payment exposure4
- OperationsCritical systems, data storage, web presence, PII volume, remote access15
- IT SupportWhether support exists, where it sits, how mature the relationship is4
- GovernanceCyber insurance, IR planning, tabletops, awareness training, program ownership7